Google dismantles botnet secretly running on 1.3 million Android TV boxes
Summary
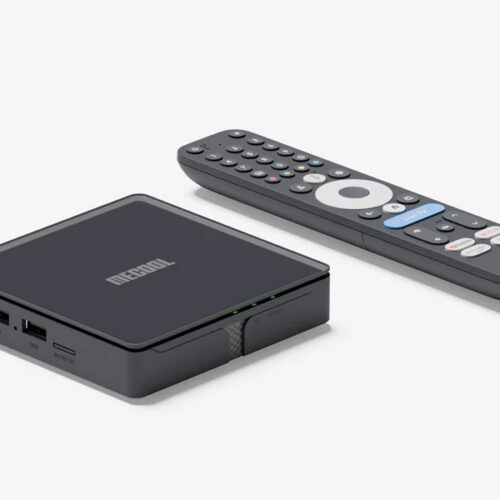
Google says it disrupted the x.cpe botnet, which infected more than 1.3 million Android TV devices, many sold under the MECOOL brand. The malware used system-level access to install modules, disable Play Protect, and support activities including residential proxy traffic and ad fraud.Key Facts
- Google worked with Japan’s National Police Agency, Synthient, and Trend Micro to disrupt the botnet.
- Google said a backdoor installed malware after affected devices were set up and connected to the internet.
- The malware’s initial stub app could contact its operators and install modules but had no malicious capabilities on its own.
- Google said Videostrong operators could run commands, capture screens, and probe devices on local networks.
- Trend Micro counted 1,472,554 infected devices, while Google described the botnet as reaching more than 1.3 million devices.
- Google said legal action shut down domains and servers used to operate and install the malware, cutting Videostrong off from about 10 million compromised devices.
- Google ended its relationship with Videostrong and barred the company and its subsidiaries from using Google’s Android apps and services.
- Google said it is changing its device certification process to address the loophole; affected devices may still have Play Protect disabled and malware modules installed.
Read the Full Article
This is a fact-based summary from The Actual News. Click below to read the complete story directly from the original source.